Security & Compliance
Lynx Compliance
One system of record for your security and privacy frameworks
lynx_compliance
· v19.0.1.11.1
· Standard
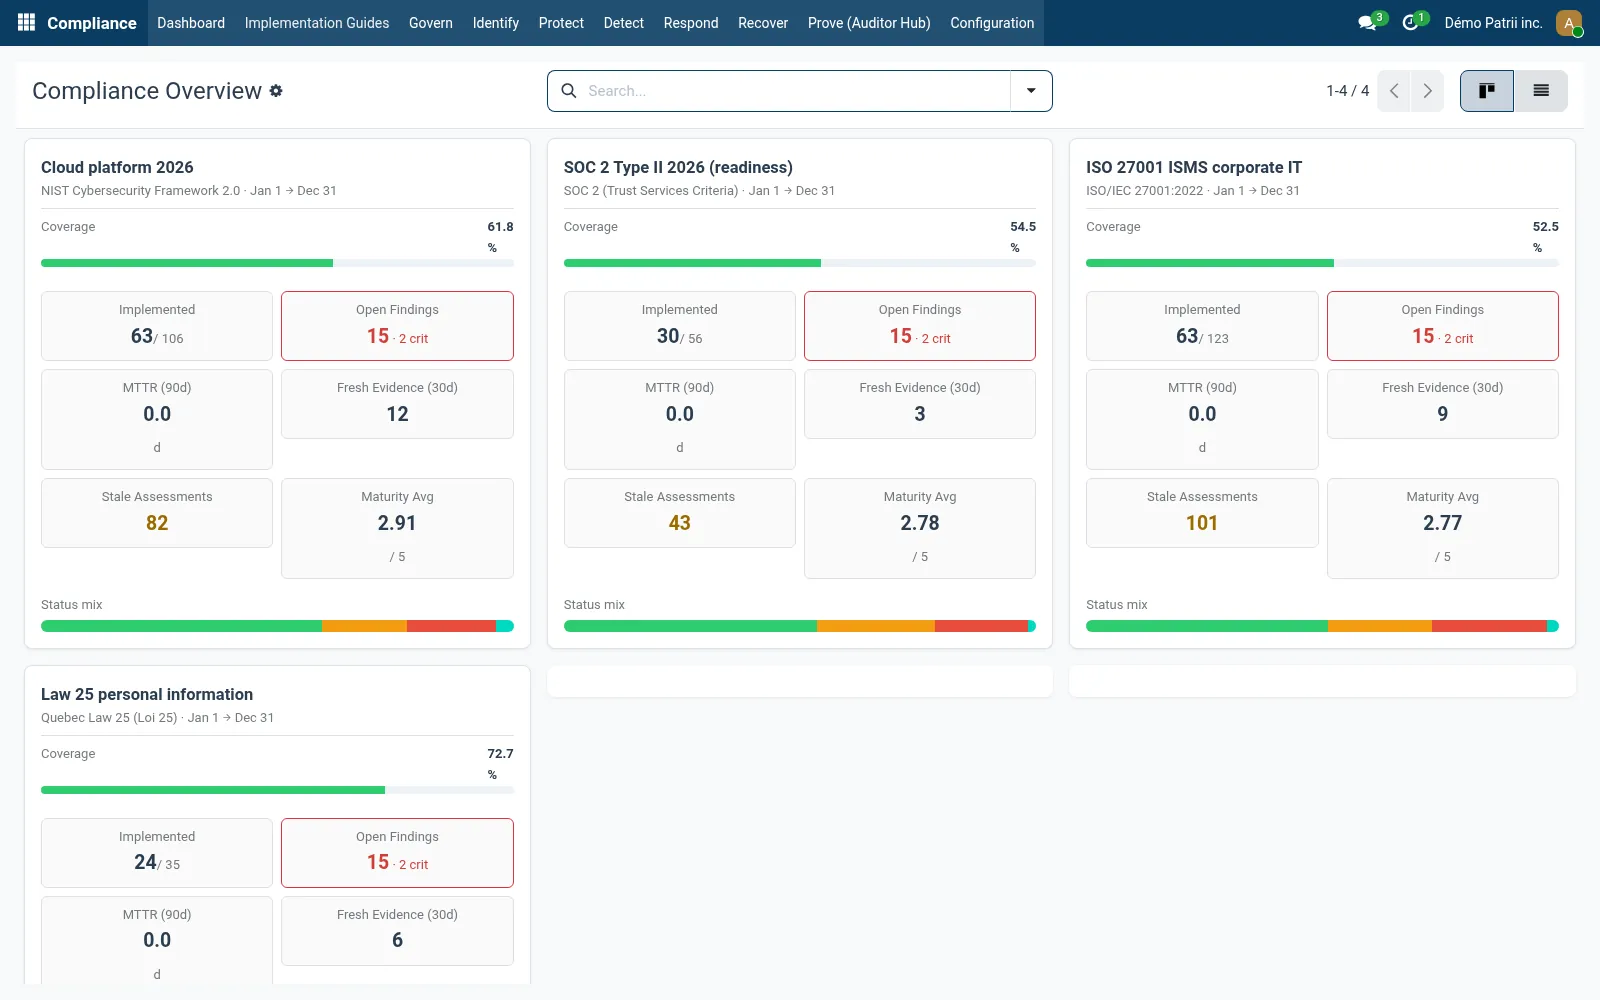
Lynx Compliance holds the frameworks you answer to (NIST CSF 2.0 is included) as data: functions, categories and controls, cross-referenced to ISO 27001, SOC 2, Quebec Law 25 and Bill C-26. Each scope you assess gets one assessment per control, with status, maturity, owner, review dates and the evidence that proves it.
Accepted evidence is sealed with a SHA-256 fingerprint, a daily scan turns gaps into findings with owners and due dates, and the coverage matrix exports to a spreadsheet or a PDF for signature.
Why teams pick it
What Lynx Compliance does for you
Framework and control registry
Frameworks, functions, categories and controls stored as records, with cross-references so one control answers several frameworks.
Assessments per scope
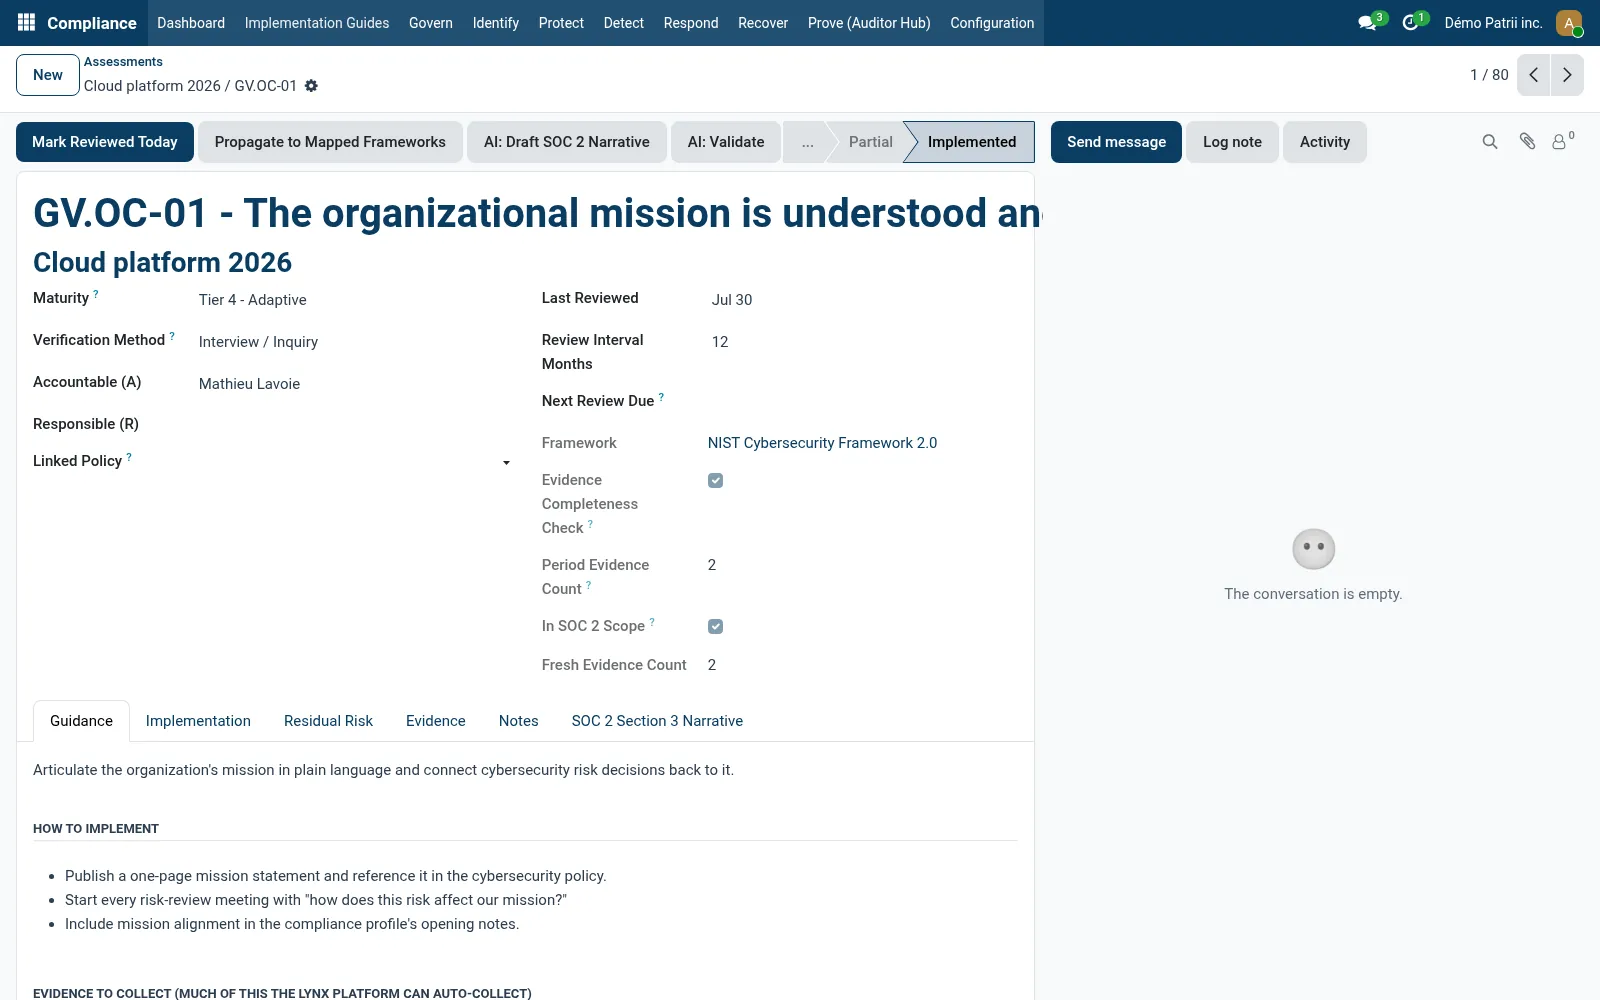
One assessment per control and scope: status, maturity tier 1 to 5, accountable and responsible people, verification method and next review.
Guidance on every control
What the control means, how to implement it, what evidence to collect and an example of residual risk, shown on the assessment.
Sealed evidence
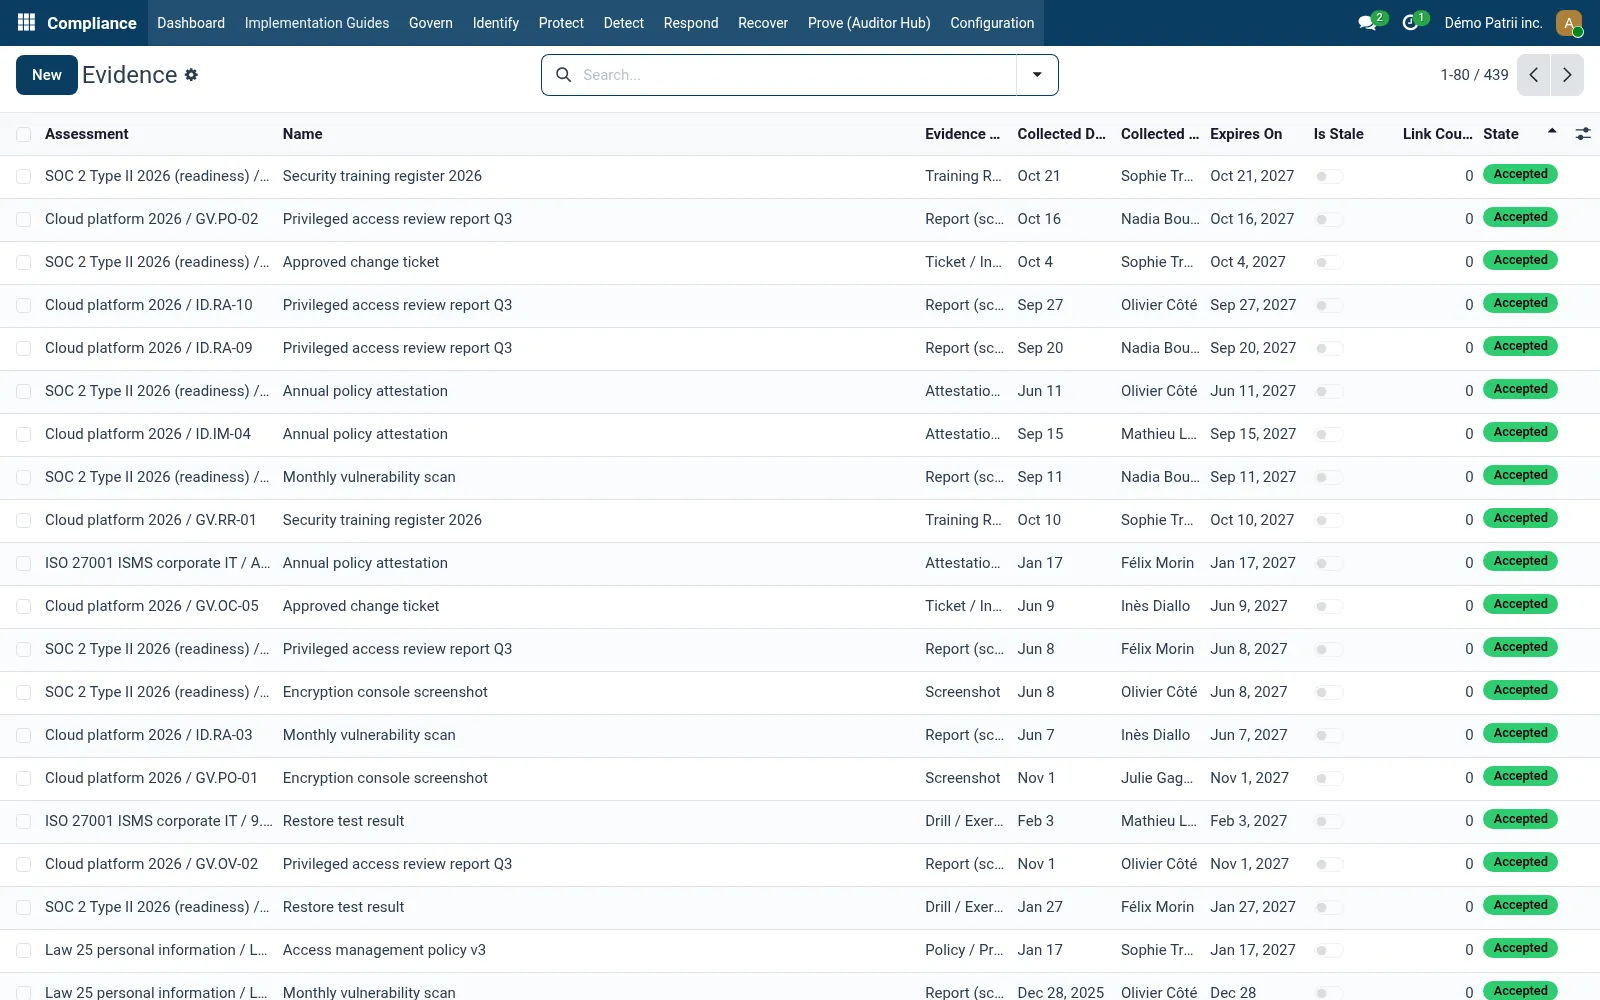
Evidence links to any record, URL or file. Once accepted it is frozen with a SHA-256 fingerprint you can re-verify, and corrections create a new version.
Findings and escalation
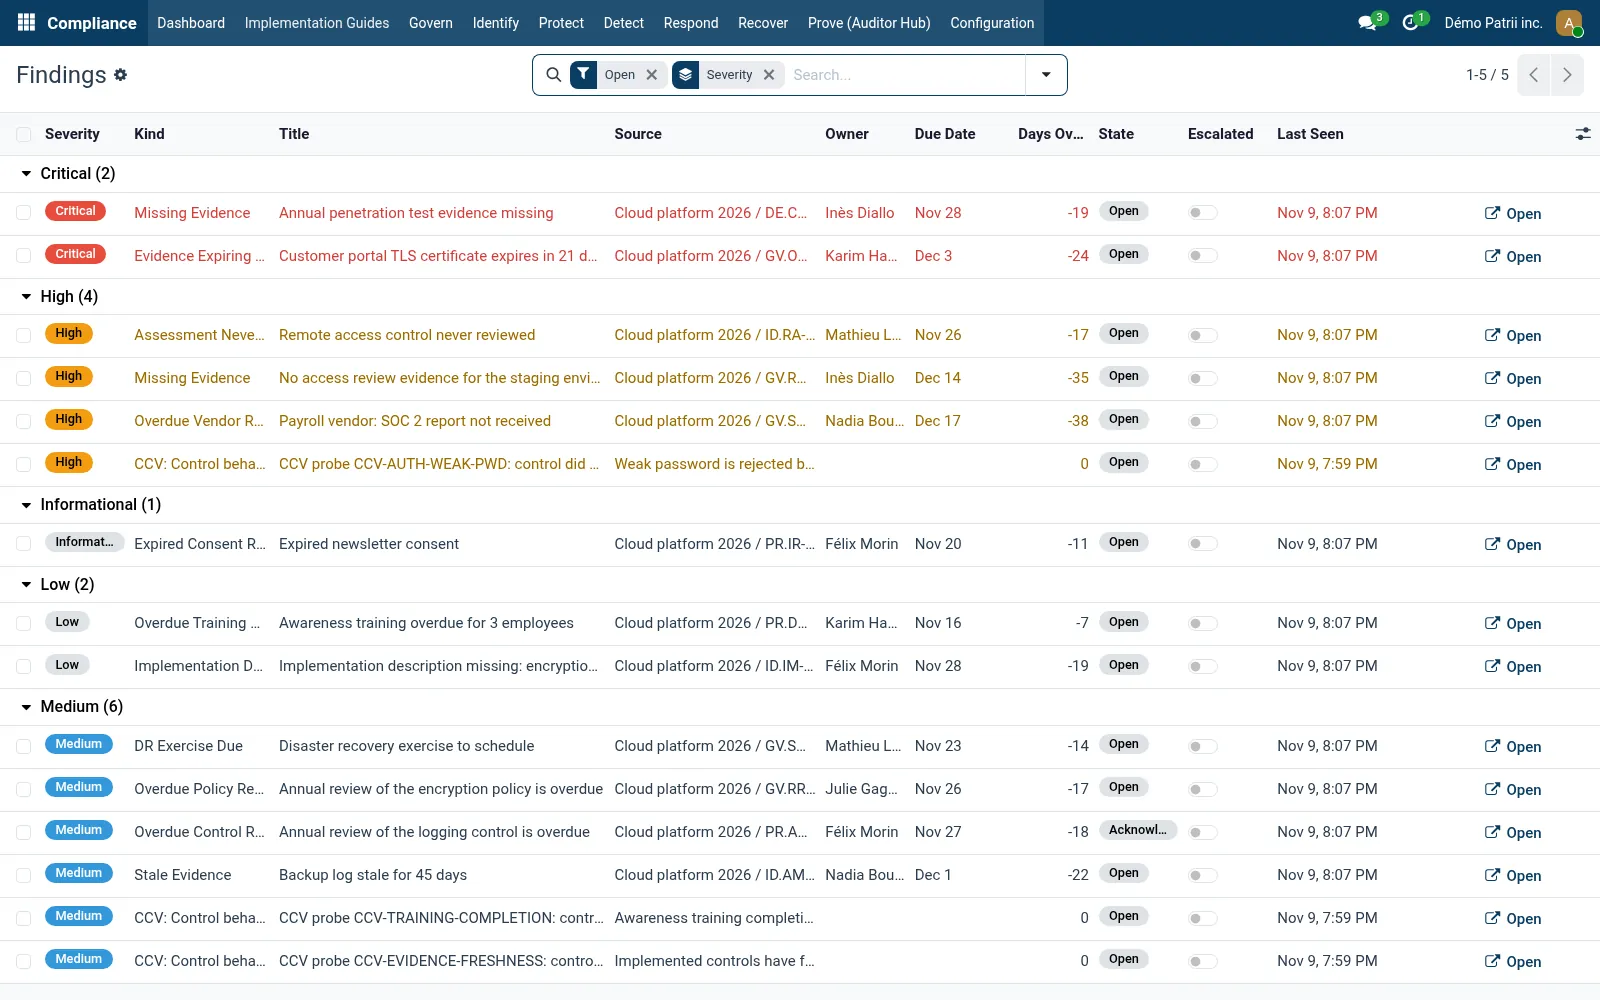
A daily scan raises findings for overdue reviews, missing or stale evidence; critical findings left open for 48 hours are escalated.
Exports for the auditor
A cross-framework coverage matrix in XLSX, and a profile report in PDF sent for signature.
Product tour
See it in action
Integrations
Lynx Compliance works with 52 other modules
Each bridge ships separately so you only install what your team uses.
Try Lynx Compliance on your team.
Free trial, no credit card. Talk to sales when you're ready.