Professional Services · Compliance
Audit-ready, every day of the year.
ISO 27001, SOC 2, Law 25 and more on one control registry, with sealed evidence, a tamper-evident audit log and a portal for your auditor, hosted in Montréal.
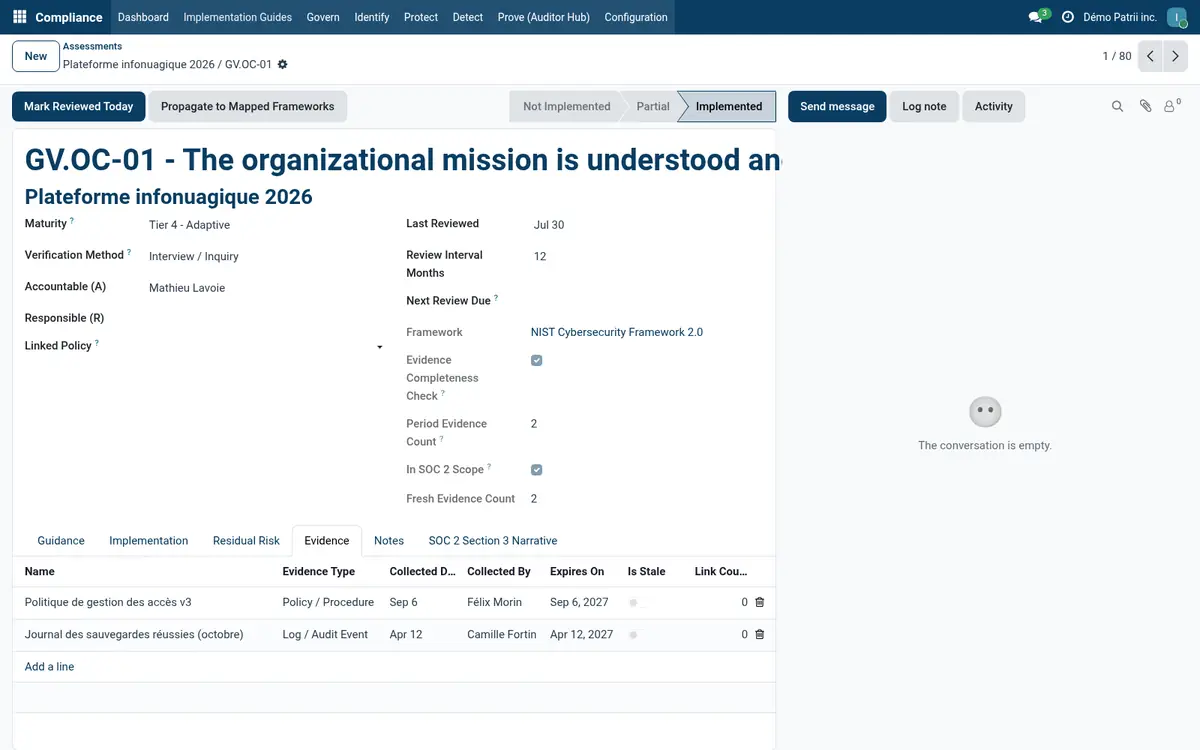
Collect once, prove it everywhere.
What Lynx does for you
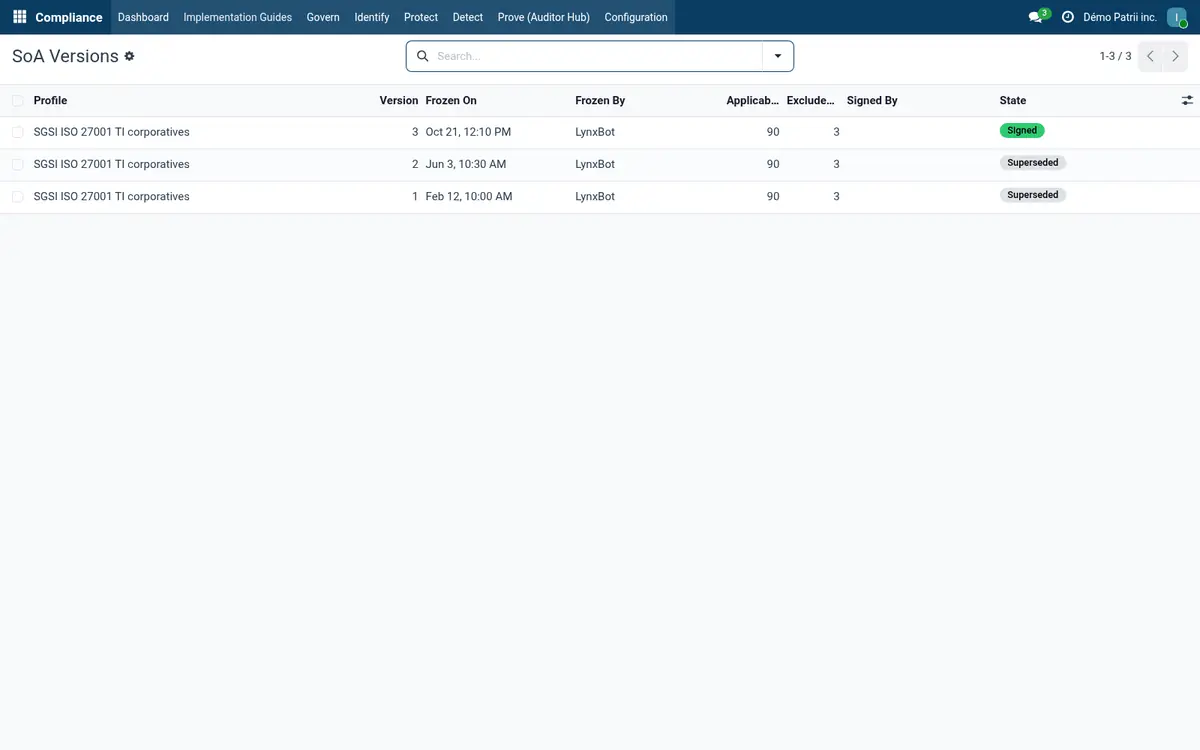
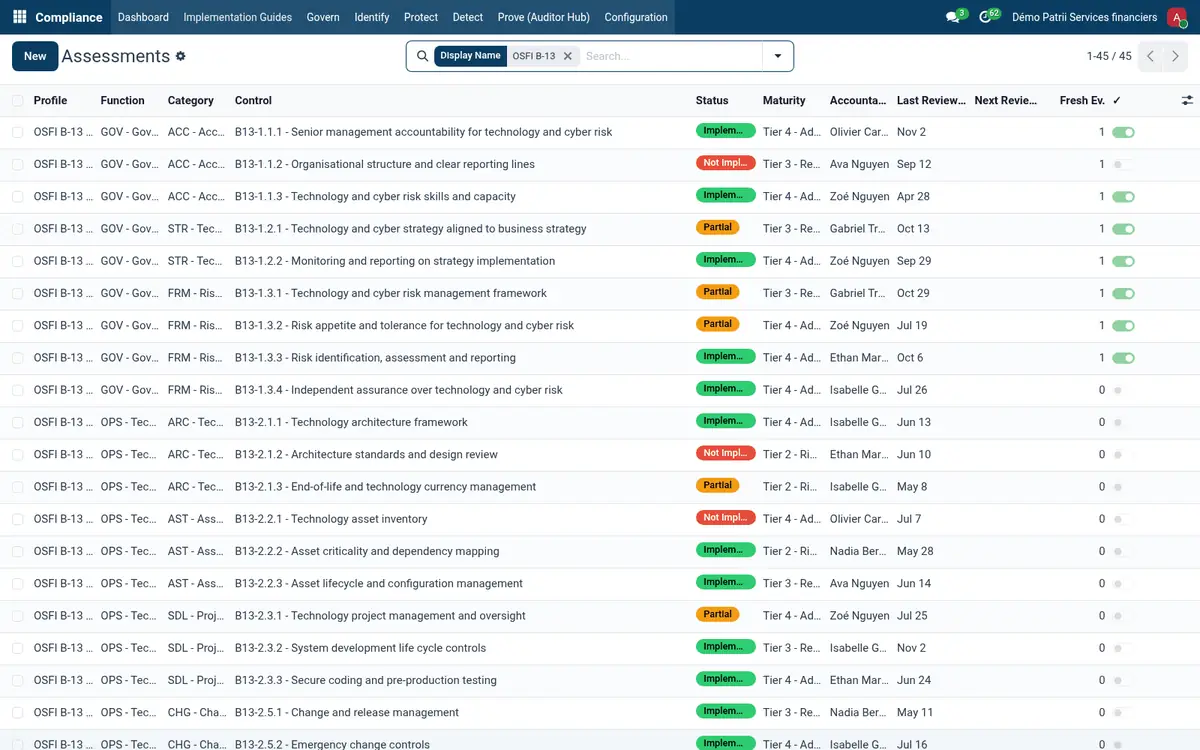
The artifacts your auditor will ask for.
Statement of Applicability frozen into signed versions carrying the SHA-256 of the PDF, re-verifiable any time. Clauses 4 to 10 as controls: scope, objectives, internal audit programme, management review, risk…
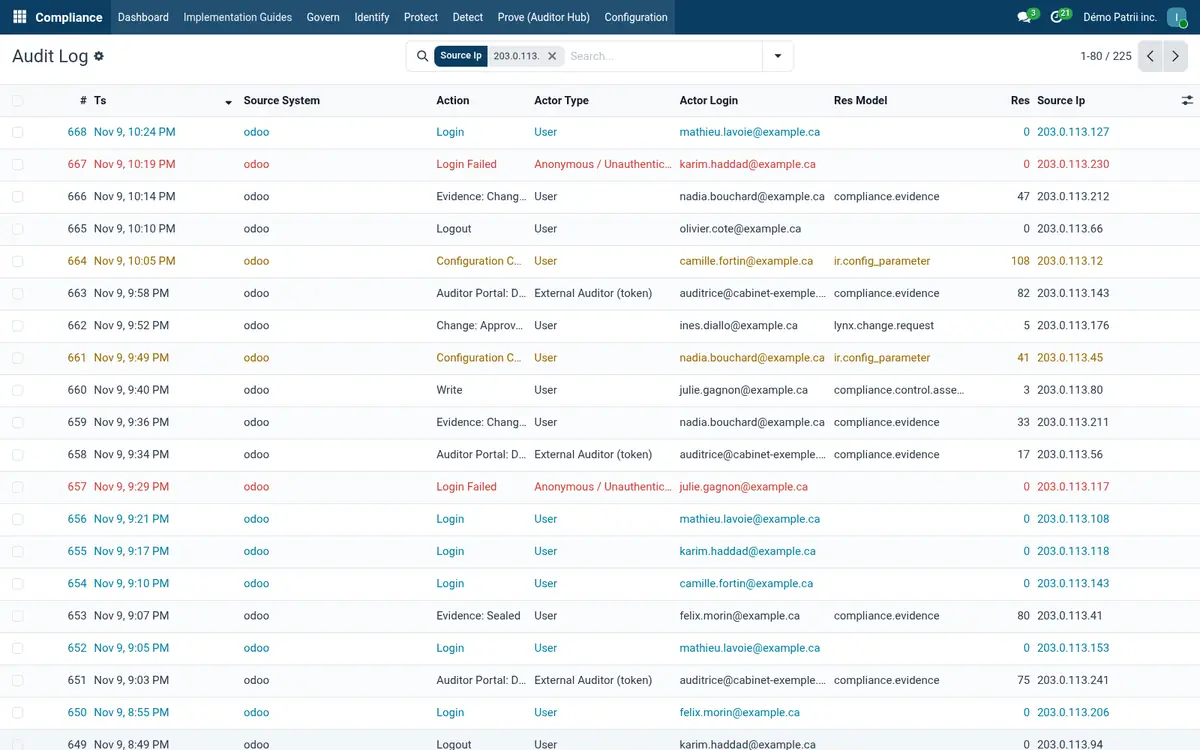
Let the auditor in. Keep the record.
Hash-chained audit log: updates and deletes revoked at the database; logins, user, group and access-rule changes recorded. Chain verification reports the first broken row; events forward to your SIEM over syslog.
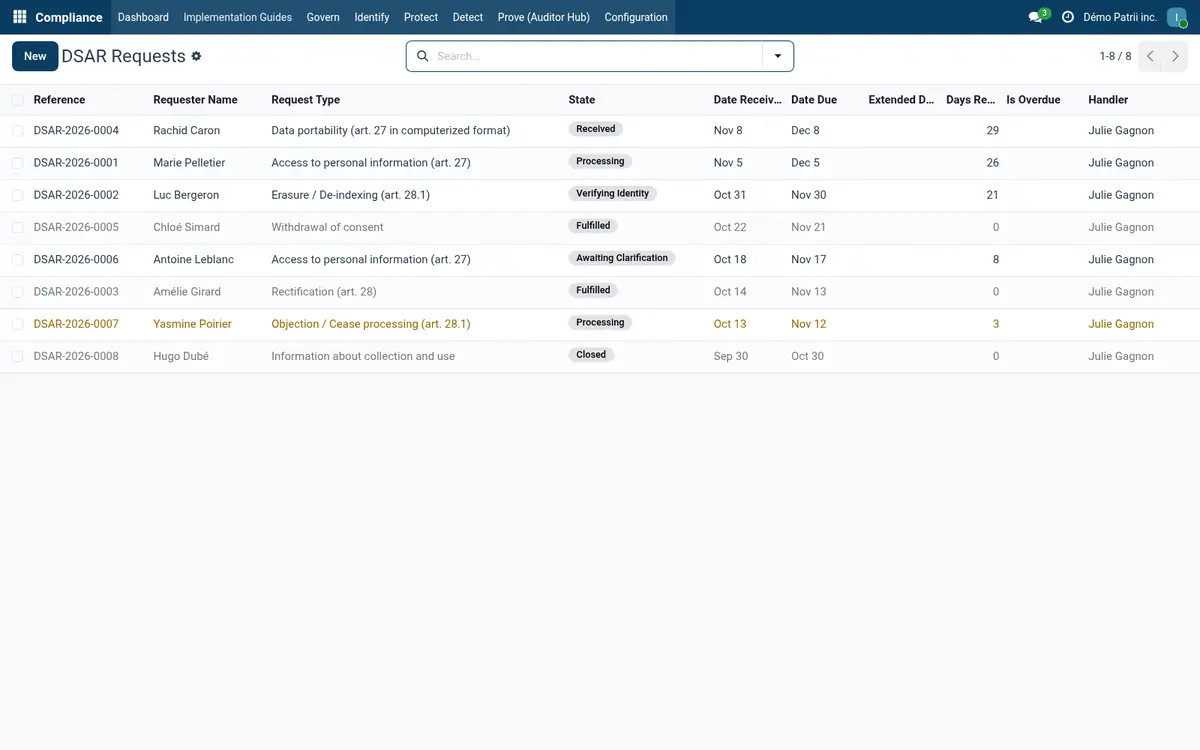
Written for Canadian privacy law, not translated to it.
Law 25: about 35 article-level controls, tagged with their 2022, 2023 and 2024 in-force dates. PIPEDA: the ten fair-information principles and breach reporting, mapped to Law 25, ISO and GDPR.
Compliance add-ons: only the frameworks you are audited against
Each framework arrives with its full control set, pre-mapped to the others you hold, so a control you satisfy once counts everywhere. Add evidence connectors to collect proof automatically from the tools you already use. Prices are public, in Canadian dollars, per year.
- ISO 27001:2022
- SOC 2
- Law 25 + PIPEDA
- ISO/IEC 27701
- PCI DSS v4.0.1
- HIPAA
- GDPR
- NIST SP 800-53
- ITSG-33 / PBMM
- Bill C-26
- Evidence connectors
- Auditor portal
- AI assist
The apps it installs
One activation installs them. Each one has its own page.

Tell us about your organization
Two minutes: we get back to you within one business day.
Also in this sector
Try Lynx with your own data.
Hosted in Montréal, bilingual, no credit card to start.