Security & Compliance
Lynx Compliance - Certification (ISO 27001 + SOC 2 mandatory artifacts)
The ISO 27001 management system records, clause by clause
lynx_compliance_certification
· v19.0.1.3.1
· Add-on
Certification adds the records an ISO 27001 management system must keep beyond the controls: scope, Statement of Applicability, internal audits and their findings, nonconformities with corrective actions, management reviews, security objectives and risk acceptance by signature.
It also covers the clause 4 to 10 registers: interested parties, risk methodology, treatment plans, competence, communication, controlled documents, audit programme and continual improvement.
Why teams pick it
What Lynx Compliance - Certification (ISO 27001 + SOC 2 mandatory artifacts) does for you
Statement of Applicability
Frozen into numbered versions with a SHA-256 fingerprint, verifiable later and sent for signature.
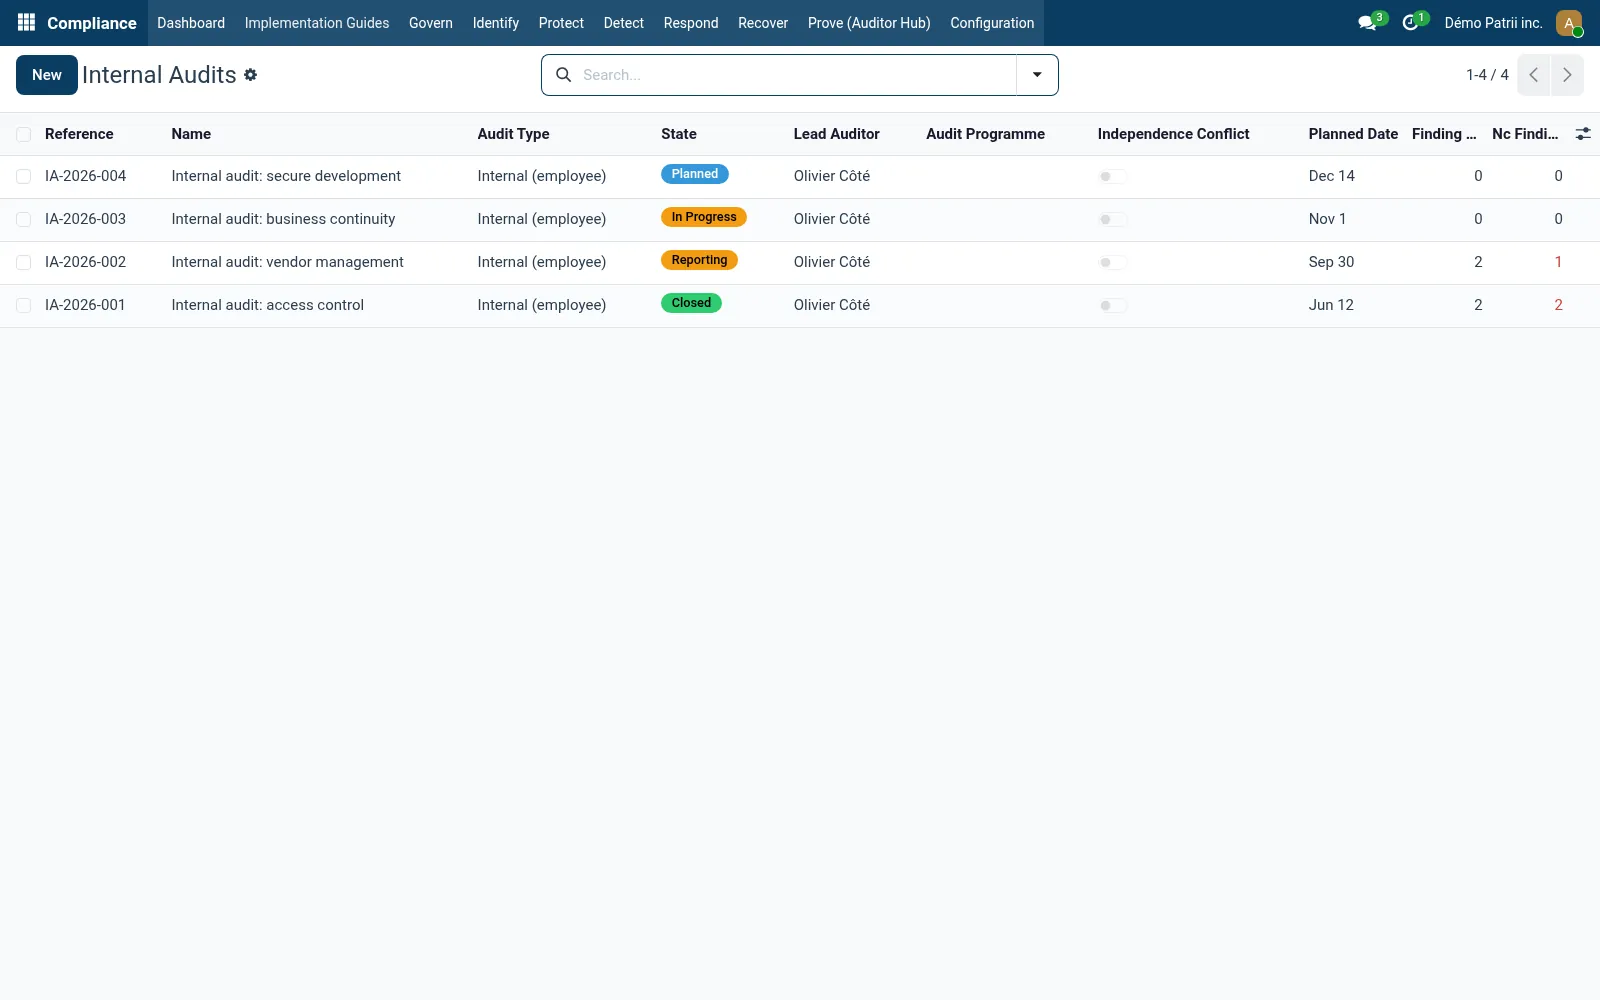
Internal audits
Audit programme, audits with scope and criteria, and findings from major nonconformity to good practice.
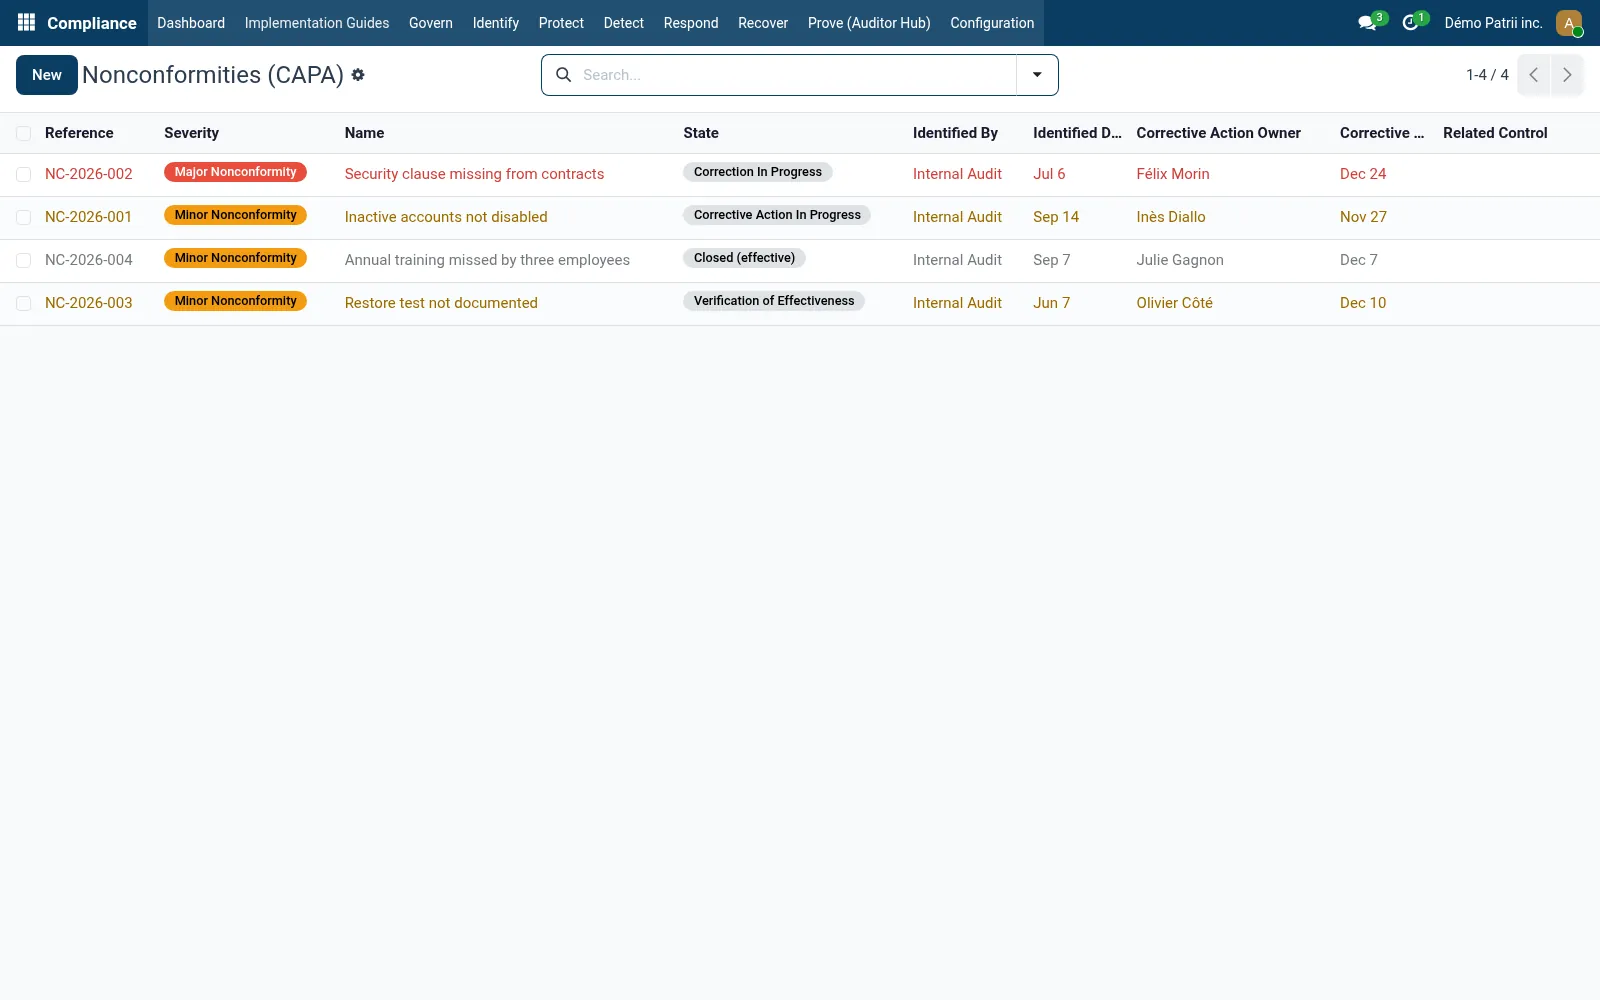
Nonconformities and corrective actions
Correction, root cause, corrective action, verification of effectiveness, from the finding to closure.
Management review
The inputs and outputs the standard lists, with attendees, decisions and action items.
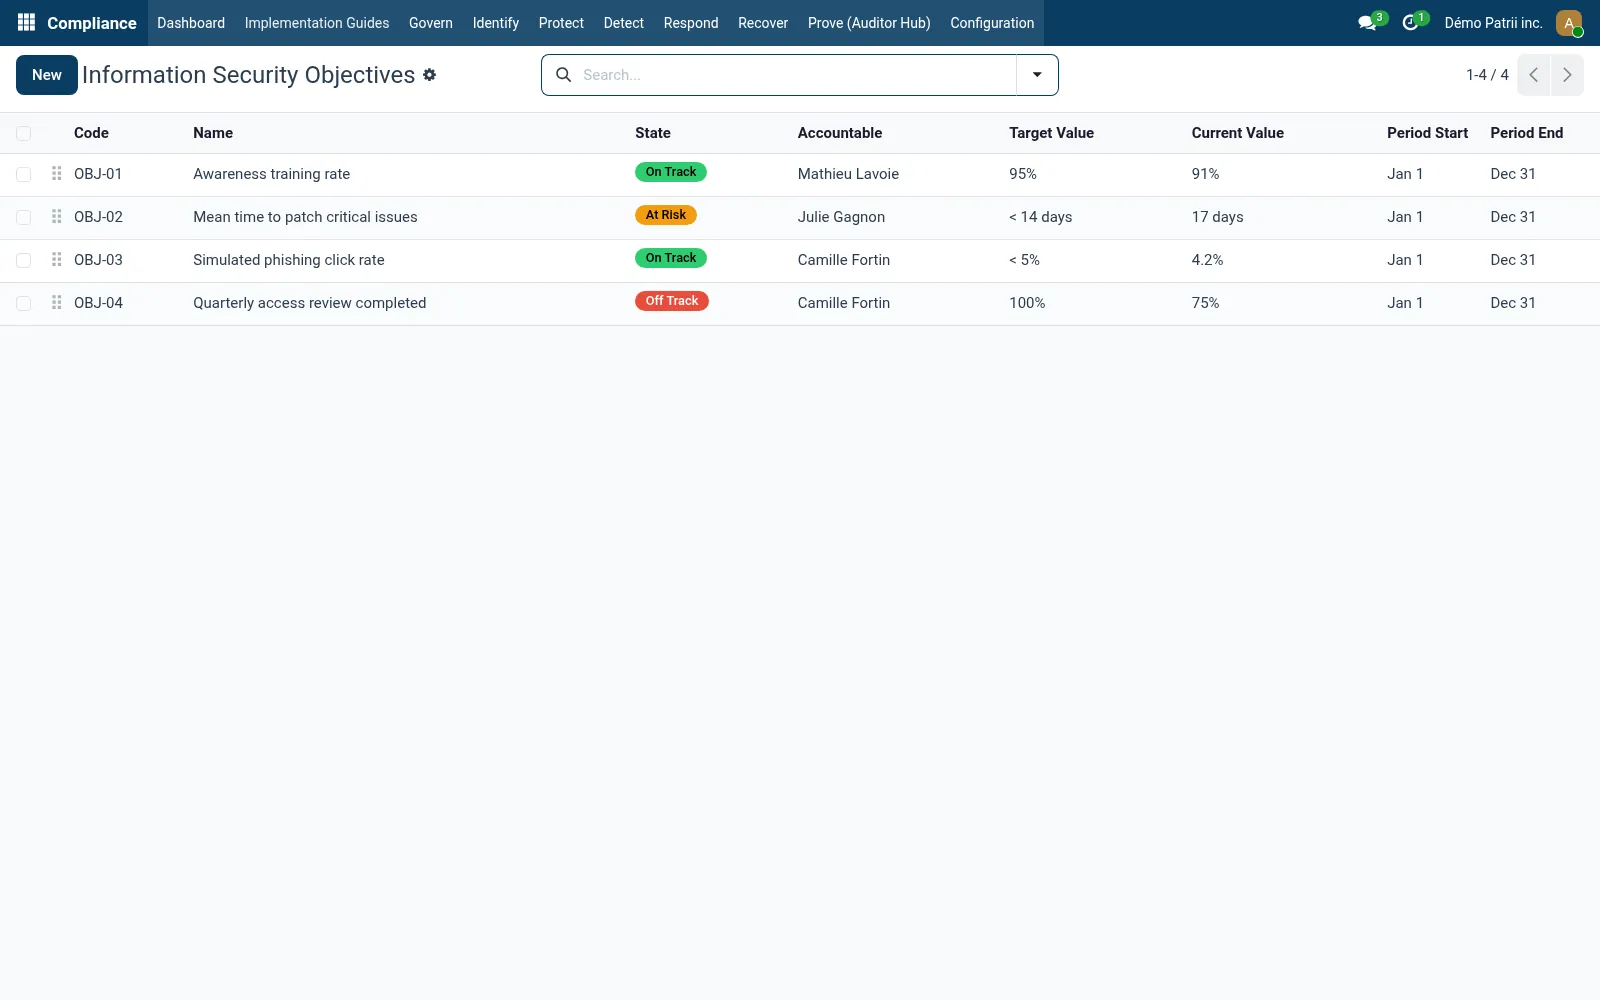
Security objectives
Target, current value and thresholds, tracked on track, at risk or off track.
Product tour
See it in action
Try Lynx Compliance - Certification (ISO 27001 + SOC 2 mandatory artifacts) on your team.
Free trial, no credit card. Talk to sales when you're ready.